Race to Update Critical Web Systems After Severe Infrastructure Flaw Found
BYTnews Investigation Desk
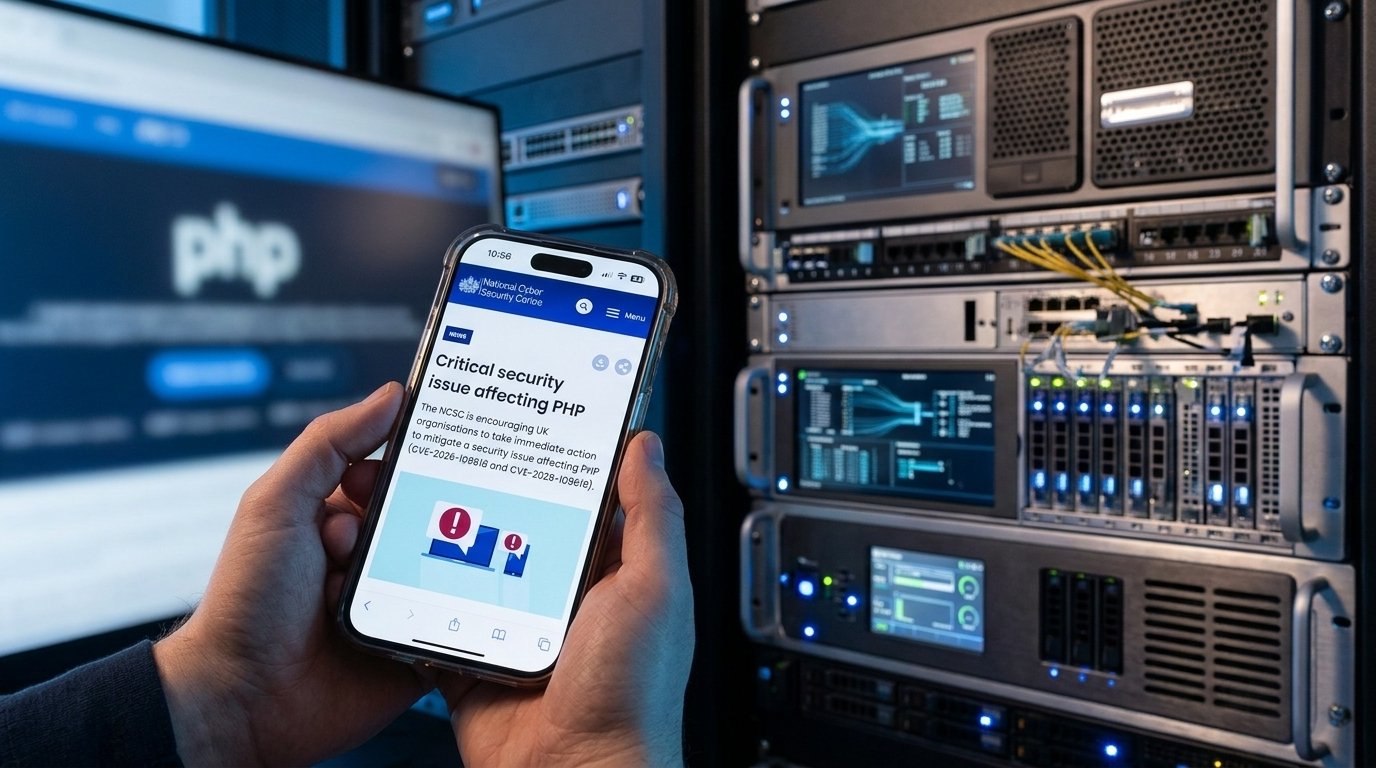
The digital world is currently locked in a frantic race against time, as cybersecurity experts, system administrators, and critical infrastructure operators worldwide scramble to deploy security patches for newly discovered, severe vulnerabilities within PHP and other core web runtime environments. These foundational technologies power an estimated 75% of the internet's infrastructure, from major social media platforms and global e-commerce sites to sensitive government portals and financial institutions. The flaws, if left unaddressed, open the door to widespread remote code execution (RCE) attacks, giving malicious actors unparalleled control over compromised servers and potentially leading to catastrophic data breaches, service disruptions, and systemic instability.
The urgency is palpable. While developers have swiftly released crucial updates, the sheer ubiquity of the affected systems means millions of servers globally are now exposed during the "window of vulnerability"—the perilous period between a patch's release and its universal application. Governments are issuing urgent advisories, financial regulators are demanding immediate action, and businesses are confronting the logistical nightmare of identifying, testing, and deploying fixes across vast and often complex digital estates before attackers can leverage these newly publicised weaknesses. The incident serves as a stark reminder of the fragile underpinnings of our interconnected digital society and the constant, high-stakes battle to secure it.
The Unseen Threat: A Deep Dive into the Flaw
The vulnerabilities, yet to be fully detailed publicly to prevent immediate mass exploitation, are understood to reside deep within the interpreters and core libraries of widely used web runtime environments, most notably PHP. While specific CVEs (Common Vulnerabilities and Exposures) are expected to follow a coordinated disclosure, preliminary reports suggest issues stemming from critical flaws such as deserialization bugs, arbitrary file write vulnerabilities, or complex type-juggling errors that can be coerced into memory corruption. These low-level flaws can be triggered through carefully crafted input processed by web applications, allowing an attacker to execute malicious code on the server itself.
Security researchers, operating under strict non-disclosure agreements, identified these weaknesses over several months, highlighting their potential for devastating impact. "These aren't just minor bugs; they're foundational cracks in the infrastructure," explained Dr. Anya Sharma, lead cybersecurity analyst at InfoSec Global, in a statement to BYTnews. "The nature of these vulnerabilities means that in many cases, an attacker doesn't even need to bypass complex authentication. Simply interacting with a vulnerable web application could be enough to gain full control."
The sheer scale of the potential impact cannot be overstated. PHP alone underpins a vast ecosystem of content management systems (CMS) like WordPress, Drupal, and Joomla, which collectively host tens of millions of websites. Beyond CMS, countless custom-built web applications, enterprise resource planning (ERP) systems, and financial platforms also rely on PHP and other runtime environments, making the attack surface astronomically large. The discovery necessitates a thorough audit and immediate patching across virtually every sector of the digital economy.
A Global Patchwork: Who's Affected and Why
The implications of these vulnerabilities span every corner of the globe and impact every organization with an online presence. The diversity and criticality of affected systems paint a concerning picture:
- Financial Institutions: Banks, investment firms, and payment processors rely heavily on secure web applications for online banking, transaction processing, and customer data management. An RCE attack here could lead to massive financial fraud, customer data theft (including account details, personal identifiable information, and transaction histories), and severe reputational damage. The integrity of the global financial system itself could be threatened if core platforms are compromised.
- Government Agencies: From national defence departments to local municipal services, government entities manage vast troves of sensitive citizen data, classified information, and critical infrastructure control systems. A successful RCE attack could result in intelligence leaks, disruption of essential public services, electoral interference, or even sabotage of national assets.
- E-commerce and Retailers: Online stores and marketplaces process billions of transactions daily and store invaluable customer data, including payment information and delivery addresses. Compromise here could lead to widespread credit card fraud, identity theft, and crippling operational downtime during peak shopping seasons, leading to significant financial losses and erosion of consumer trust.
- Healthcare Providers: Hospitals, clinics, and insurance companies manage highly sensitive patient health information (PHI). An RCE vulnerability could expose patient records, facilitate medical identity theft, and disrupt critical care services, with potential life-threatening consequences.
- Cloud Service Providers: Many cloud services operate on underlying infrastructure that utilizes these vulnerable web technologies. A flaw exploited at this level could have a cascading effect, compromising thousands of client applications and data simultaneously, regardless of their individual security postures.
- Small and Medium-sized Businesses (SMBs): Often lacking dedicated cybersecurity teams or resources, SMBs are particularly vulnerable. They may be slower to patch, making them easy targets for opportunistic attackers seeking to build botnets, launch ransomware attacks, or steal customer lists.
The interconnectedness of the digital world means that a compromise in one sector can quickly ripple through others. A successful attack on a third-party vendor, for example, could provide a stepping stone into numerous client organizations, underscoring the critical need for supply chain security vigilance.
The Urgent Mandate: Securing the Digital Frontier
The immediate aftermath of such a critical vulnerability disclosure is always characterized by intense activity within the cybersecurity community. For system administrators, IT managers, and security operations centres (SOCs) globally, this translates into an all-out sprint to identify, assess, and mitigate risk.
The primary directive is clear: patch immediately. However, this is often easier said than done. Large enterprises operate complex environments with thousands of servers, diverse operating systems, and myriad custom applications. Identifying every instance of a vulnerable PHP interpreter or web runtime environment, testing the compatibility of new patches with existing applications to avoid breaking critical services, and then coordinating deployment across multiple teams and geographic locations presents a formidable challenge.
"Our teams are working around the clock," noted a senior IT director at a major European bank, who requested anonymity due to the sensitivity of the situation. "We've got staging environments running simulations, but the sheer volume of dependencies means any patch deployment is a high-stakes operation. The attackers know this, and they're not waiting for us to finish our testing."
Indeed, malicious actors are notoriously quick to weaponize newly disclosed vulnerabilities. Automated scanning tools are already combing the internet for unpatched systems, often within hours or even minutes of a patch's release. This creates a dangerously narrow "window of vulnerability" where even a slight delay in patching can expose an organization to significant risk. Threat intelligence reports indicate a surge in suspicious network activity targeting web servers, suggesting active exploitation attempts are already underway.
RCE Explained: The Hacker's Ultimate Weapon
Remote Code Execution (RCE) is one of the most severe types of software vulnerabilities, often considered the "holy grail" for attackers. In simple terms, an RCE flaw allows an attacker to remotely execute arbitrary commands or code on a vulnerable server or system.
Here's how it generally works and its devastating consequences:
- Vulnerability Exploitation: An attacker identifies a flaw in a web application or its underlying runtime environment (like PHP). This flaw might be in how the system processes user input, handles specific data types, or manages memory.
- Payload Delivery: The attacker crafts a specific input (known as a "payload") that, when processed by the vulnerable system, doesn't just trigger an error but instead causes the system to interpret a part of the input as executable code.
- Code Execution: The server, unknowingly, executes the attacker's code. This code could be anything from simple commands to complex scripts designed to install malware, create new user accounts, or completely reconfigure the system.
The consequences of a successful RCE attack are profound:
- Complete System Compromise: The attacker gains full control over the compromised server, often with the same privileges as the legitimate server owner.
- Data Theft: Access to databases, files, and credentials stored on the server, leading to breaches of sensitive personal, financial, or proprietary information.
- System Defacement or Destruction: Websites can be altered, services can be shut down, or entire systems can be wiped.
- Ransomware Deployment: Attackers can encrypt all data on the server and demand a ransom for its release.
- Botnet Recruitment: Compromised servers can be coerced into becoming part of a botnet, used to launch further attacks like Distributed Denial of Service (DDoS) against other targets.
- Lateral Movement: The compromised server can serve as a pivot point to gain access to other systems within the internal network.
For organizations, an RCE attack is not merely a breach; it's a complete loss of control, potentially leading to irreparable damage.
Fortifying Defenses: A Call to Action
While immediate patching is the paramount first step, a comprehensive security strategy extends far beyond mere updates. Organizations must adopt a multi-layered approach to fortify their digital infrastructure against not just these specific vulnerabilities but the constant deluge of emerging threats.
- Immediate Patching: Prioritize and deploy the latest security patches for PHP and all affected web runtime environments across all development, staging, and production servers.
- Asset Inventory and Management: Maintain an up-to-date and accurate inventory of all web-facing assets, their software versions, and dependencies. This is crucial for quickly identifying all affected systems.
- Web Application Firewalls (WAFs): Implement and configure WAFs to detect and block malicious requests attempting to exploit known or unknown vulnerabilities. While not a silver bullet, WAFs can provide an additional layer of protection, particularly during the window of vulnerability.
- Intrusion Detection/Prevention Systems (IDPS): Deploy IDPS to monitor network traffic for suspicious patterns and block known attack signatures.
- Network Segmentation: Isolate critical systems and sensitive data from less-trusted network segments. This can limit the lateral movement of an attacker even if an RCE is achieved on one system.
- Principle of Least Privilege: Ensure that web servers and applications run with the minimum necessary permissions. This reduces the scope of damage an attacker can inflict if they gain control.
- Regular Security Audits and Penetration Testing: Proactively seek out vulnerabilities through independent security assessments and ethical hacking exercises.
- Logging and Monitoring: Implement robust logging across all web servers and applications, and actively monitor these logs for unusual activity, error messages, or signs of compromise. Utilize Security Information and Event Management (SIEM) systems for centralized analysis.
- Incident Response Plan: Have a well-defined and rehearsed incident response plan in place to rapidly detect, contain, eradicate, and recover from a successful attack.
#### Technical Mitigation Table
| Action | Description | Priority |
| :------------------------------ | :------------------------------------------------------------------------------------------------------------------------------------------------------- | :------- |
| Apply Security Patches | Immediately update PHP versions and core web runtime environments to the latest security releases provided by vendors. | Critical |
| Deploy WAF Rules | Configure Web Application Firewalls (WAFs) with updated rulesets to detect and block known exploit attempts targeting the new vulnerabilities. | High |
| Network Segmentation | Isolate web servers hosting critical applications from internal networks and sensitive data stores to limit lateral movement in case of compromise. | High |
| Principle of Least Privilege| Review and enforce that web server processes and application user accounts operate with the absolute minimum necessary permissions. | High |
| Enhanced Logging & Monitoring| Increase logging verbosity on web servers and scrutinize logs for unusual activity, failed requests, or suspicious command execution attempts. | Medium |
| Vulnerability Scanning | Conduct urgent internal and external vulnerability scans to identify all affected assets and confirm patch deployment. | Medium |
| Backup Critical Data | Ensure recent, immutable backups of all critical data and configurations are available to facilitate rapid recovery in case of data loss or encryption. | Medium |
Beyond the Patch: A Recurring Challenge
The current crisis highlights a fundamental tension at the heart of the digital age: the constant evolution of software and the inherent potential for undiscovered flaws. As software becomes more complex and interconnected, the surface area for attack grows exponentially. This incident, while severe, is merely the latest in a long line of critical vulnerabilities affecting foundational internet technologies.
The open-source nature of many core web components, including PHP, offers immense benefits in terms of innovation and collaborative development. However, it also means that vulnerabilities, when found, often exist in millions of installations simultaneously. The responsibility for security then becomes a shared burden between developers, who must adhere to secure coding practices and conduct rigorous audits, and users, who must prioritize timely updates and robust security hygiene.
Moving forward, there's a clear need for:
- Increased Investment in Security Research: Proactive efforts to discover and address vulnerabilities before they are exploited by malicious actors.
- Automated Security Testing: Integration of security checks throughout the software development lifecycle (DevSecOps) to catch flaws early.
- Threat Intelligence Sharing: Enhanced collaboration between governments, industry, and academia to share information about emerging threats and mitigation strategies.
- User Education: Continuous education for system administrators and end-users on the importance of regular updates and best security practices.
Frequently Asked Questions
FAQ 1: What exactly is a "core web runtime environment" and why is it so critical?
A core web runtime environment refers to the underlying software framework that allows web applications to execute on a server. Think of it as the engine that powers a website or web service. For example, PHP is a scripting language that runs within a specific runtime environment (like PHP-FPM or Apache's mod_php) to generate dynamic web content. Other examples include Node.js for JavaScript applications, Python's WSGI servers, or Ruby on Rails' Puma/Unicorn. These environments are critical because they are the first point of interaction between a user's browser (or an attacker's tool) and the server's operating system and data. They process user requests, connect to databases, and execute application logic. If a vulnerability exists within this core environment, it can bypass security measures within the application itself, giving an attacker direct access to the server's resources. Because they sit at such a fundamental level, compromising them often grants high privileges, making the entire server, and potentially the entire network, vulnerable.
**FAQ 2: How can organizations ensure they identify all vulnerable systems, especially in complex environments?**
Identifying all vulnerable systems in a complex enterprise environment is a significant challenge, but several strategies can help:
- Comprehensive Asset Inventory: Maintain a detailed, up-to-date inventory of all servers, applications, and their software versions. This should include both externally facing and internal systems. Tools for automated asset discovery and configuration management databases (CMDBs) are essential here.
- Automated Vulnerability Scanning: Regularly run authenticated and unauthenticated vulnerability scanners across the entire network. Authenticated scans provide deeper insights by logging into systems and checking software versions directly, while unauthenticated scans simulate external attack scenarios.
- Code Auditing: For custom applications, perform static application security testing (SAST) and dynamic application security testing (DAST) to identify code-level vulnerabilities within the application and its dependencies.
- Network Mapping: Use network discovery tools to map out all active devices and services, helping to uncover forgotten or shadow IT systems that might be running vulnerable software.
- Dependency Scanning: Tools that scan project dependencies (e.g., Composer for PHP, npm for Node.js) can identify vulnerable libraries or components used within applications.
- Cloud Visibility: For cloud-native environments, leverage cloud security posture management (CSPM) tools to gain visibility into cloud assets and their configurations.
The key is a continuous process of discovery, assessment, and remediation, rather than a one-time effort.
FAQ 3: What are the long-term implications of such critical infrastructure flaws for global cybersecurity?
The long-term implications of critical infrastructure flaws like these are multi-faceted and profound:
- Erosion of Trust: Repeated incidents of widespread vulnerabilities erode public and business trust in the security of online services, potentially hindering digital adoption and innovation.
- Increased Regulatory Scrutiny: Governments and regulatory bodies will likely impose stricter compliance requirements, data protection laws, and mandatory breach reporting, increasing the burden on organizations.
- Shifting Security Paradigms: It reinforces the need for a "assume breach" mentality and a move towards more resilient, "zero-trust" architectures where no user or system is implicitly trusted, regardless of their location.
- Supply Chain Security Focus: Organizations will increasingly demand higher security standards from their software vendors and third-party providers, leading to more rigorous vetting processes and contractual obligations.
- Resource Strain: The constant need to patch, monitor, and defend against sophisticated threats places immense strain on limited cybersecurity talent and financial resources globally.
- Geopolitical Instability: Nation-state actors actively seek out and weaponize such vulnerabilities, posing significant risks to critical national infrastructure, military systems, and democratic processes, potentially exacerbating international tensions.
- Demand for Secure-by-Design: There will be a sustained push for developers to prioritize security from the initial design phase of software (Secure by Design) rather than retrofitting security measures. This requires investment in secure coding education and robust development frameworks.
Ultimately, these flaws highlight the perpetual arms race between defenders and attackers, underscoring that cybersecurity is not a destination but an ongoing, complex journey requiring constant vigilance and adaptive strategies.
The race to secure the internet's bedrock against these severe vulnerabilities is a defining moment for global cybersecurity. It underscores the fragility of our interconnected digital ecosystem and the imperative for collective, decisive action. As patches are deployed and systems are hardened, the digital world watches with bated breath, hoping that the defenders can outpace the attackers in this critical sprint for online safety and stability. The ongoing vigilance and proactive measures taken today will determine the resilience of our digital future.