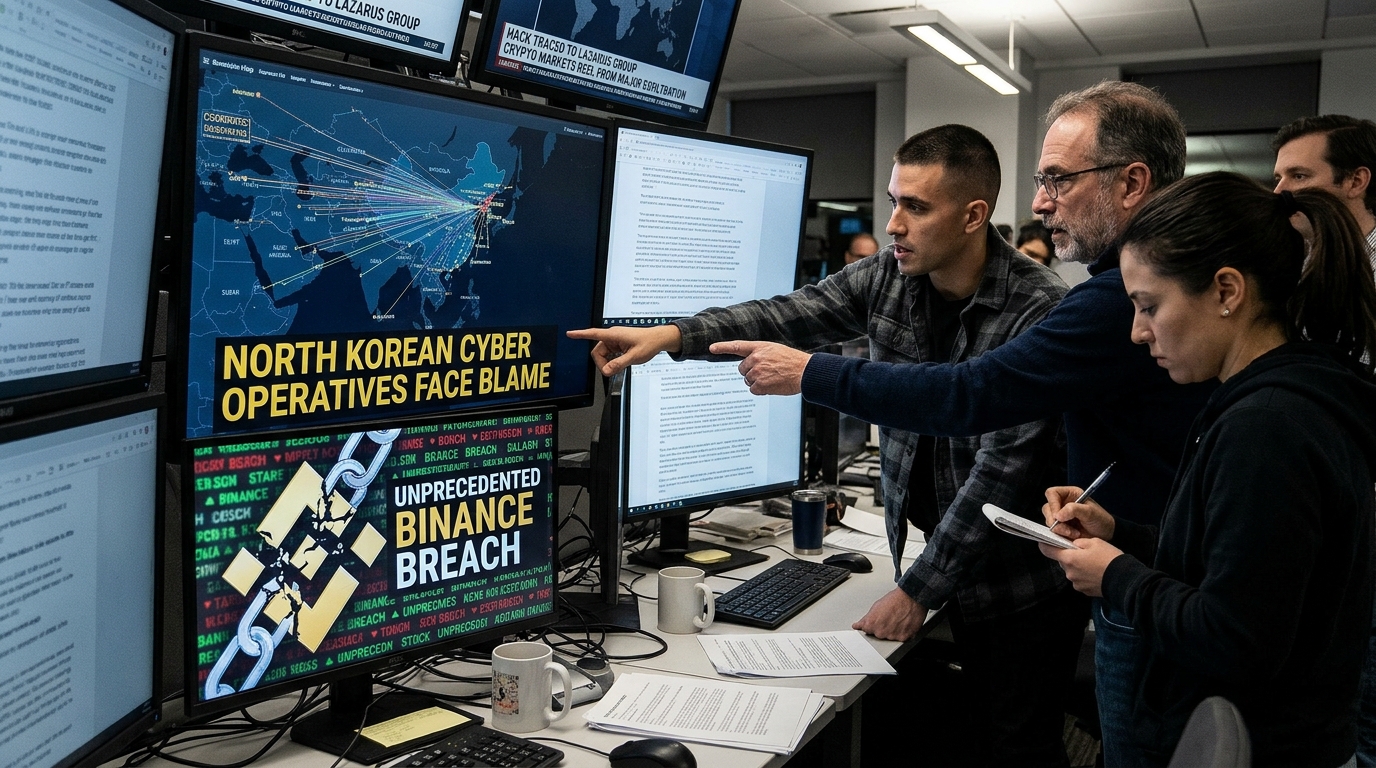
Suspected North Korean state actors stand accused of executing a record-making intrusion against crypto exchange Binance, according to reporting from BBC News. Investigators point toward elite hacking squads whose growing technical strength now threatens major centralized trading infrastructure.
Key Takeaways
- Investigators suspect North Korean state hackers breached Binance in an unprecedented, record-making heist.
- The attack scale reveals advanced technical capabilities among state-directed cyber teams targeting digital assets.
- Centralized crypto exchanges must deploy hardware isolation protocols to withstand relentless foreign intelligence operations.
Why are North Korean squads the prime suspects in the Binance breach?
Security analysts focus on North Korean operatives because their attack patterns match specialized intrusion methods refined over years of financial espionage. BBC News reports that investigators treat these elite teams as the primary suspects behind the massive Binance heist, citing technical hallmarks consistent with state-directed cyber commands.
These cyber units operate under direct government mandates to generate revenue, bypassing global economic sanctions. In our experience tracking major security threats, sophisticated crews bypass perimeter defenses by targeting internal communication channels and administrative credentials. They compromise privileged system accounts, alter settlement pipelines, and drain centralized liquidity pools before defenses react.
- Threat profile monitoring: Review administrative session logs across all crypto custody accounts weekly to detect anomalous permission escalations.
How do state-backed hackers compromise centralized cryptocurrency platforms?
Advanced threat teams penetrate cryptocurrency exchanges by exploiting human access points rather than brute-forcing core cryptographic ledgers. Once hackers breach an employee workstation via tailored phishing or malicious code, they pivot across internal subnetworks toward signature services. This lateral movement lets attackers authorize fraudulent transfers directly through legitimate infrastructure.
State-sponsored intruders then fragment the stolen funds across hundreds of intermediate wallets to frustrate forensic tracking. We've seen how automated transaction mixers obscure flow paths, complicating recovery efforts for compliance teams. The resulting operational paralysis prevents rapid containment, allowing attackers to withdraw significant capital before operators can freeze affected digital assets.
- Asset isolation protocol: Move trading balances into multi-signature cold wallets that require physical authorization keys from separated geographic locations.
What does this major heist mean for institutional digital security?
The incident demonstrates that standard network boundaries fail against persistent, state-funded adversaries targeting high-value financial platforms. As reported by BBC News, the record-making Binance intrusion reveals how powerful and capable these specialized state hackers have become. Centralized systems now face adversaries with resources comparable to modern intelligence agencies.
Financial institutions must transition from reactive perimeter security to continuous authorization models. When attackers possess the capability to breach top-tier global exchanges, ordinary protective measures no longer suffice. Platforms must isolate critical transaction signing from everyday office environments, ensuring that no single compromised credential can authorize massive capital transfers.
- Critical access audit: Require independent hardware security modules for every large-value transaction approval to stop unauthorized automated withdrawals.
FAQ
What evidence connects North Korea to the Binance attack?
BBC News reports that investigators suspect elite North Korean hackers due to intrusion signatures matching known state campaigns. Analysts track specific toolsets, command servers, and specialized laundering procedures that align with historical cyber operations directed by the Pyongyang regime against international financial targets.
Did the Binance intrusion compromise private user keys?
Centralized cryptocurrency platforms generally manage user funds through pooled reserves rather than individual private keys stored on customer devices. While the record-making heist targeted Binance infrastructure directly, end-user personal wallets remain protected as long as individual login credentials and authentication factors stay secure.
How can crypto exchange users safeguard their assets?
You should minimize account exposure by transferring funds not actively traded into personal hardware wallets. Enable hardware-based two-factor authentication, set strict withdrawal limits, and whitelist trusted transfer addresses so compromised platform accounts cannot instantly drain your capital during sudden institutional security emergencies.
Securing digital assets against state-level threat actors demands structural isolation, verified authentication, and proactive surveillance across every operational layer. As forensic teams continue tracking the Binance compromise, trading platforms worldwide must re-engineer access controls to withstand relentless state-directed cyber operations.
Stay informed with accurate, up-to-date global news coverage.
Sources
- Why North Korea's 'elite' hackers are the prime suspect in major Binance hack (BBC News): https://www.bbc.co.uk/news/articles/ck9dz3v7z7v3o?at_medium=RSS&at_campaign=rss